How we encrypt, sign, and let you self-host the whole control plane.
Caldyr ships standard cryptographic primitives — Ed25519 signatures over a hash chain, per-team key wrapping — and publishes your company's audit public key. Nothing here is unique magic; the value is in the integration and the operational guarantees.
Where it runs
What you can verify yourself.
Not "we promise". Cryptographic proof. Auditable cryptography. Self-hostable when your auditor demands it.
Which keys you hold, and which we do
- Personal vault: end-to-end encrypted, key never leaves your browser
- Argon2id passphrase → master key
- Optional WebAuthn auto-unlock
- Team data: per-team key held by our custody service, which can decrypt it
- No escrow on your personal note vault; escrow does exist for team keys
We sign everything
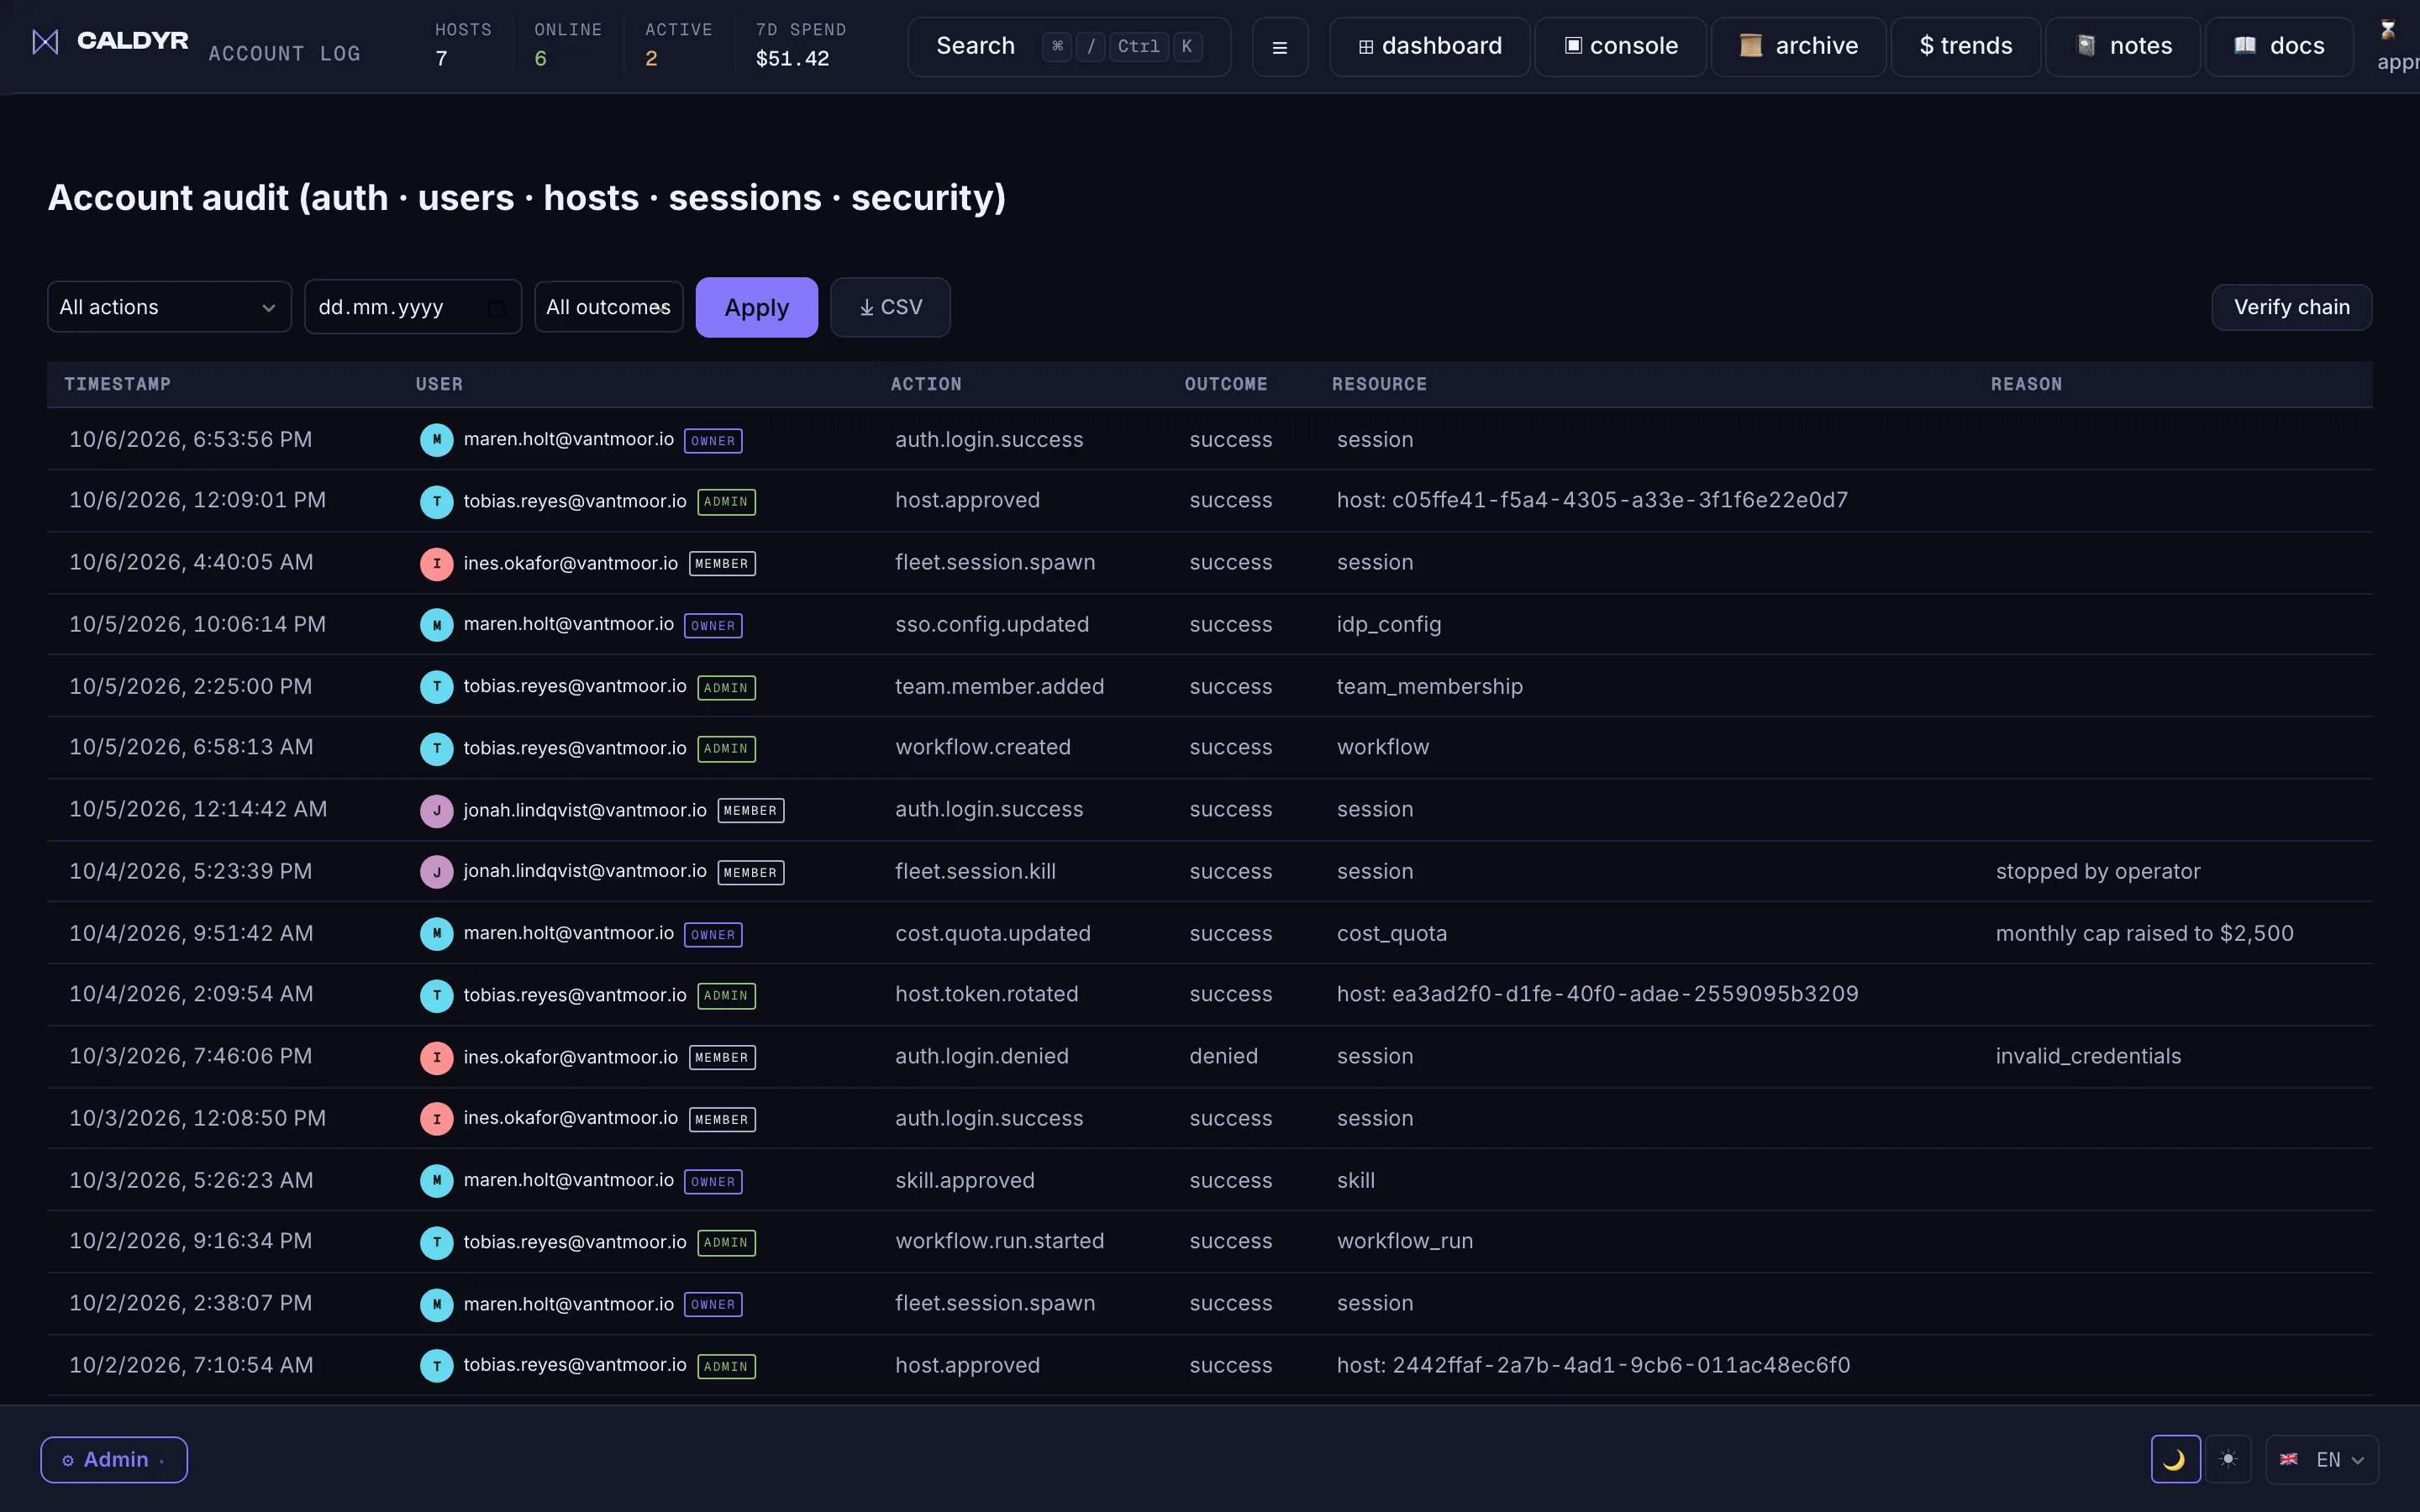
- Per-company Ed25519 audit chain
- Tamper-evident row hash chain
- Public per-company pubkey endpoint
- SIEM push auth (Enterprise): none, bearer, mTLS, JWT or Sentinel OAuth2 / shared key
- Cryptographically signed releases
Air-gap if you want
- Self-hosted signed mega-tarball
- Customer-supplied license JWS
- Caddy internal CA bootstrap
- Update server polled, never push
- Zero third-party telemetry: the control plane phones nothing home
Verify it yourself
A real 5-row sample audit chain, embedded right in this page. Recompute every SHA-256 hash, check every Ed25519 signature, live, in your browser, right now.
| ts | event | prev_hash | hash | sig | status |
|---|---|---|---|---|---|
| 2026-06-30T09:12:04Z | session.spawn | 00000000…000000 | 1fc9478e…d23310 | OyglWI4l…HbCQ== | |
| 2026-06-30T09:14:51Z | permission.approved | 1fc9478e…d23310 | f51cd7d3…62b875 | DJELgYNW…mFBQ== | |
| 2026-06-30T09:21:37Z | secret.access | f51cd7d3…62b875 | 0951657e…440f92 | kkygR5aa…eyBA== | |
| 2026-06-30T09:44:02Z | policy.updated | 0951657e…440f92 | 5fd659a7…20aa98 | e4dkZY5U…lkCA== | |
| 2026-06-30T10:03:19Z | session.closed | 5fd659a7…20aa98 | 99022532…b4952f | MFUtvbrJ…6vCw== |
Not verified yet; press Verify chain.
What we can and cannot see
Four different claims get collapsed into one word too often: encrypted in transit, encrypted at rest, processed as plaintext by the application, and end-to-end encrypted. Only the last means we cannot read it. Here is the split, per data class, for the managed service.
| Data class | Can Caldyr read it? |
|---|---|
| Personal vault notes | No. Encrypted in your browser; the note key is wrapped only to your own key and is never escrowed. Sign-in uses OPAQUE: your browser proves it knows the passphrase without sending it or a hash of it, and we store only a registration record we cannot open. Caveat: the code that derives your keys runs in your browser but is delivered by our server, so this holds for the code as served. |
| Secrets | Yes. You send the value readable; we encrypt it at rest under a per-team key our custody service can unwrap, and it returns the plaintext to the service that needs it. |
| Team knowledge base | Yes. Bodies are encrypted at rest under the team key; titles, tags and the search embeddings are stored unencrypted so entries can be listed and searched. |
| Saved session transcripts | Depends on the account. Solo (no team): the host seals agent output under a key derived from your note key before upload, so we cannot read it; only the content-free state, cost and completion events are stored readable. Team, standard mode: encrypted at rest under the team key and decrypted through custody for replay, so yes. Team in end-to-end mode: sealed on the host, we cannot read it. |
| What you type into a session | No, for Solo sessions and for teams in end-to-end mode. Your browser seals what you type and the spawn prompt before it leaves, under a key derived from your note key (Solo) or the team key; the host opens it and we relay ciphertext. Inputs are numbered, so the host refuses a replayed one. We still see that input was sent, when, and its size. Teams outside the mode, and Solo sessions started by a workflow, an API exec call or before this shipped, keep plaintext input protected by tenant isolation and access control. |
| Live session streams and replay keyframes | Yes. Live frames pass through the hub as plaintext so they can be watched in real time; stored replay keyframes are encrypted at rest under the team key. |
| Audit log rows | Yes. Audit rows are hash-chained and Ed25519-signed, not encrypted, and we hold the signing key. Their value is that you can verify them, not that we cannot change them. |
| Session metadata and account details | Yes. Host, user, team, timings, status, account email and company name are ordinary columns protected by row-level security. For Solo and end-to-end team sessions the session's descriptive record is sealed in the client and we cannot read it. Card details stay with the payment processor. |
Self-hosted and air-gapped
The cryptography is the same code path. What changes is who "we" means: on a self-hosted install the server anchor keypair is generated on your own host at install time and never reaches us, so the party that can unwrap team keys is your operator, not ours. Air-gapped installs verify the release signature and the licence offline; nothing calls back to us. Choosing a cloud model backend still sends prompts to that model provider.
This table describes the application layer. Transport is TLS everywhere and host storage is encrypted at rest; neither of those makes data unreadable to the service that operates it.
If you've evaluated alternatives, here's how we line up.
| Anthropic Console | Caldyr | |
|---|---|---|
| Per-team budgets | ◐ org only | ✓ |
| Audit signing chain (Ed25519) | ✗ | ✓ |
| SIEM push (Enterprise) | ✗ | ✓ |
| Self-host air-gapped | ✗ | ✓ |
| End-to-end encrypted personal vault | N/A | ✓ |
| Session replay (xterm) | ✗ | ✓ |
| SCIM 2.0 provisioning (Enterprise) | ◐ | ✓ |
| Time to first agent | hours | ≈ 10 min after approval |
| LLM Gateways | Caldyr | |
|---|---|---|
| Layer governed | model API request / response | agent execution on the host |
| Per-session capture + xterm replay | – | ✓ |
| Transcript encrypted at rest (per-team key) | – | ✓ |
| Signed audit chain (Ed25519) | access logs | ✓ |
| Host enrolment + per-team RBAC | – | ✓ |
| Cost attribution | per API key | per repo · team · session |
| Self-host air-gap | some | ✓ |
Complementary, not competitive: gateways route the API traffic; Caldyr proves who ran which agent, on what, under whose key, and caps the spend. Run on top of any gateway.
| Build it yourself | Caldyr | |
|---|---|---|
| Per-team budgets | ✗ | ✓ |
| Audit signing chain (Ed25519) | build it | ✓ |
| SIEM push (Enterprise) | ✗ | ✓ |
| Self-host air-gapped | depends | ✓ |
| End-to-end encrypted personal vault | depends | ✓ |
| Session replay (xterm) | ✗ | ✓ |
| SCIM 2.0 provisioning (Enterprise) | ✗ | ✓ |
| Time to first agent | weeks | ≈ 10 min after approval |
Give your auditors proof, not promises.
No obligation, just a 30-minute walkthrough. Your keys, your data, and signed evidence for your auditors.