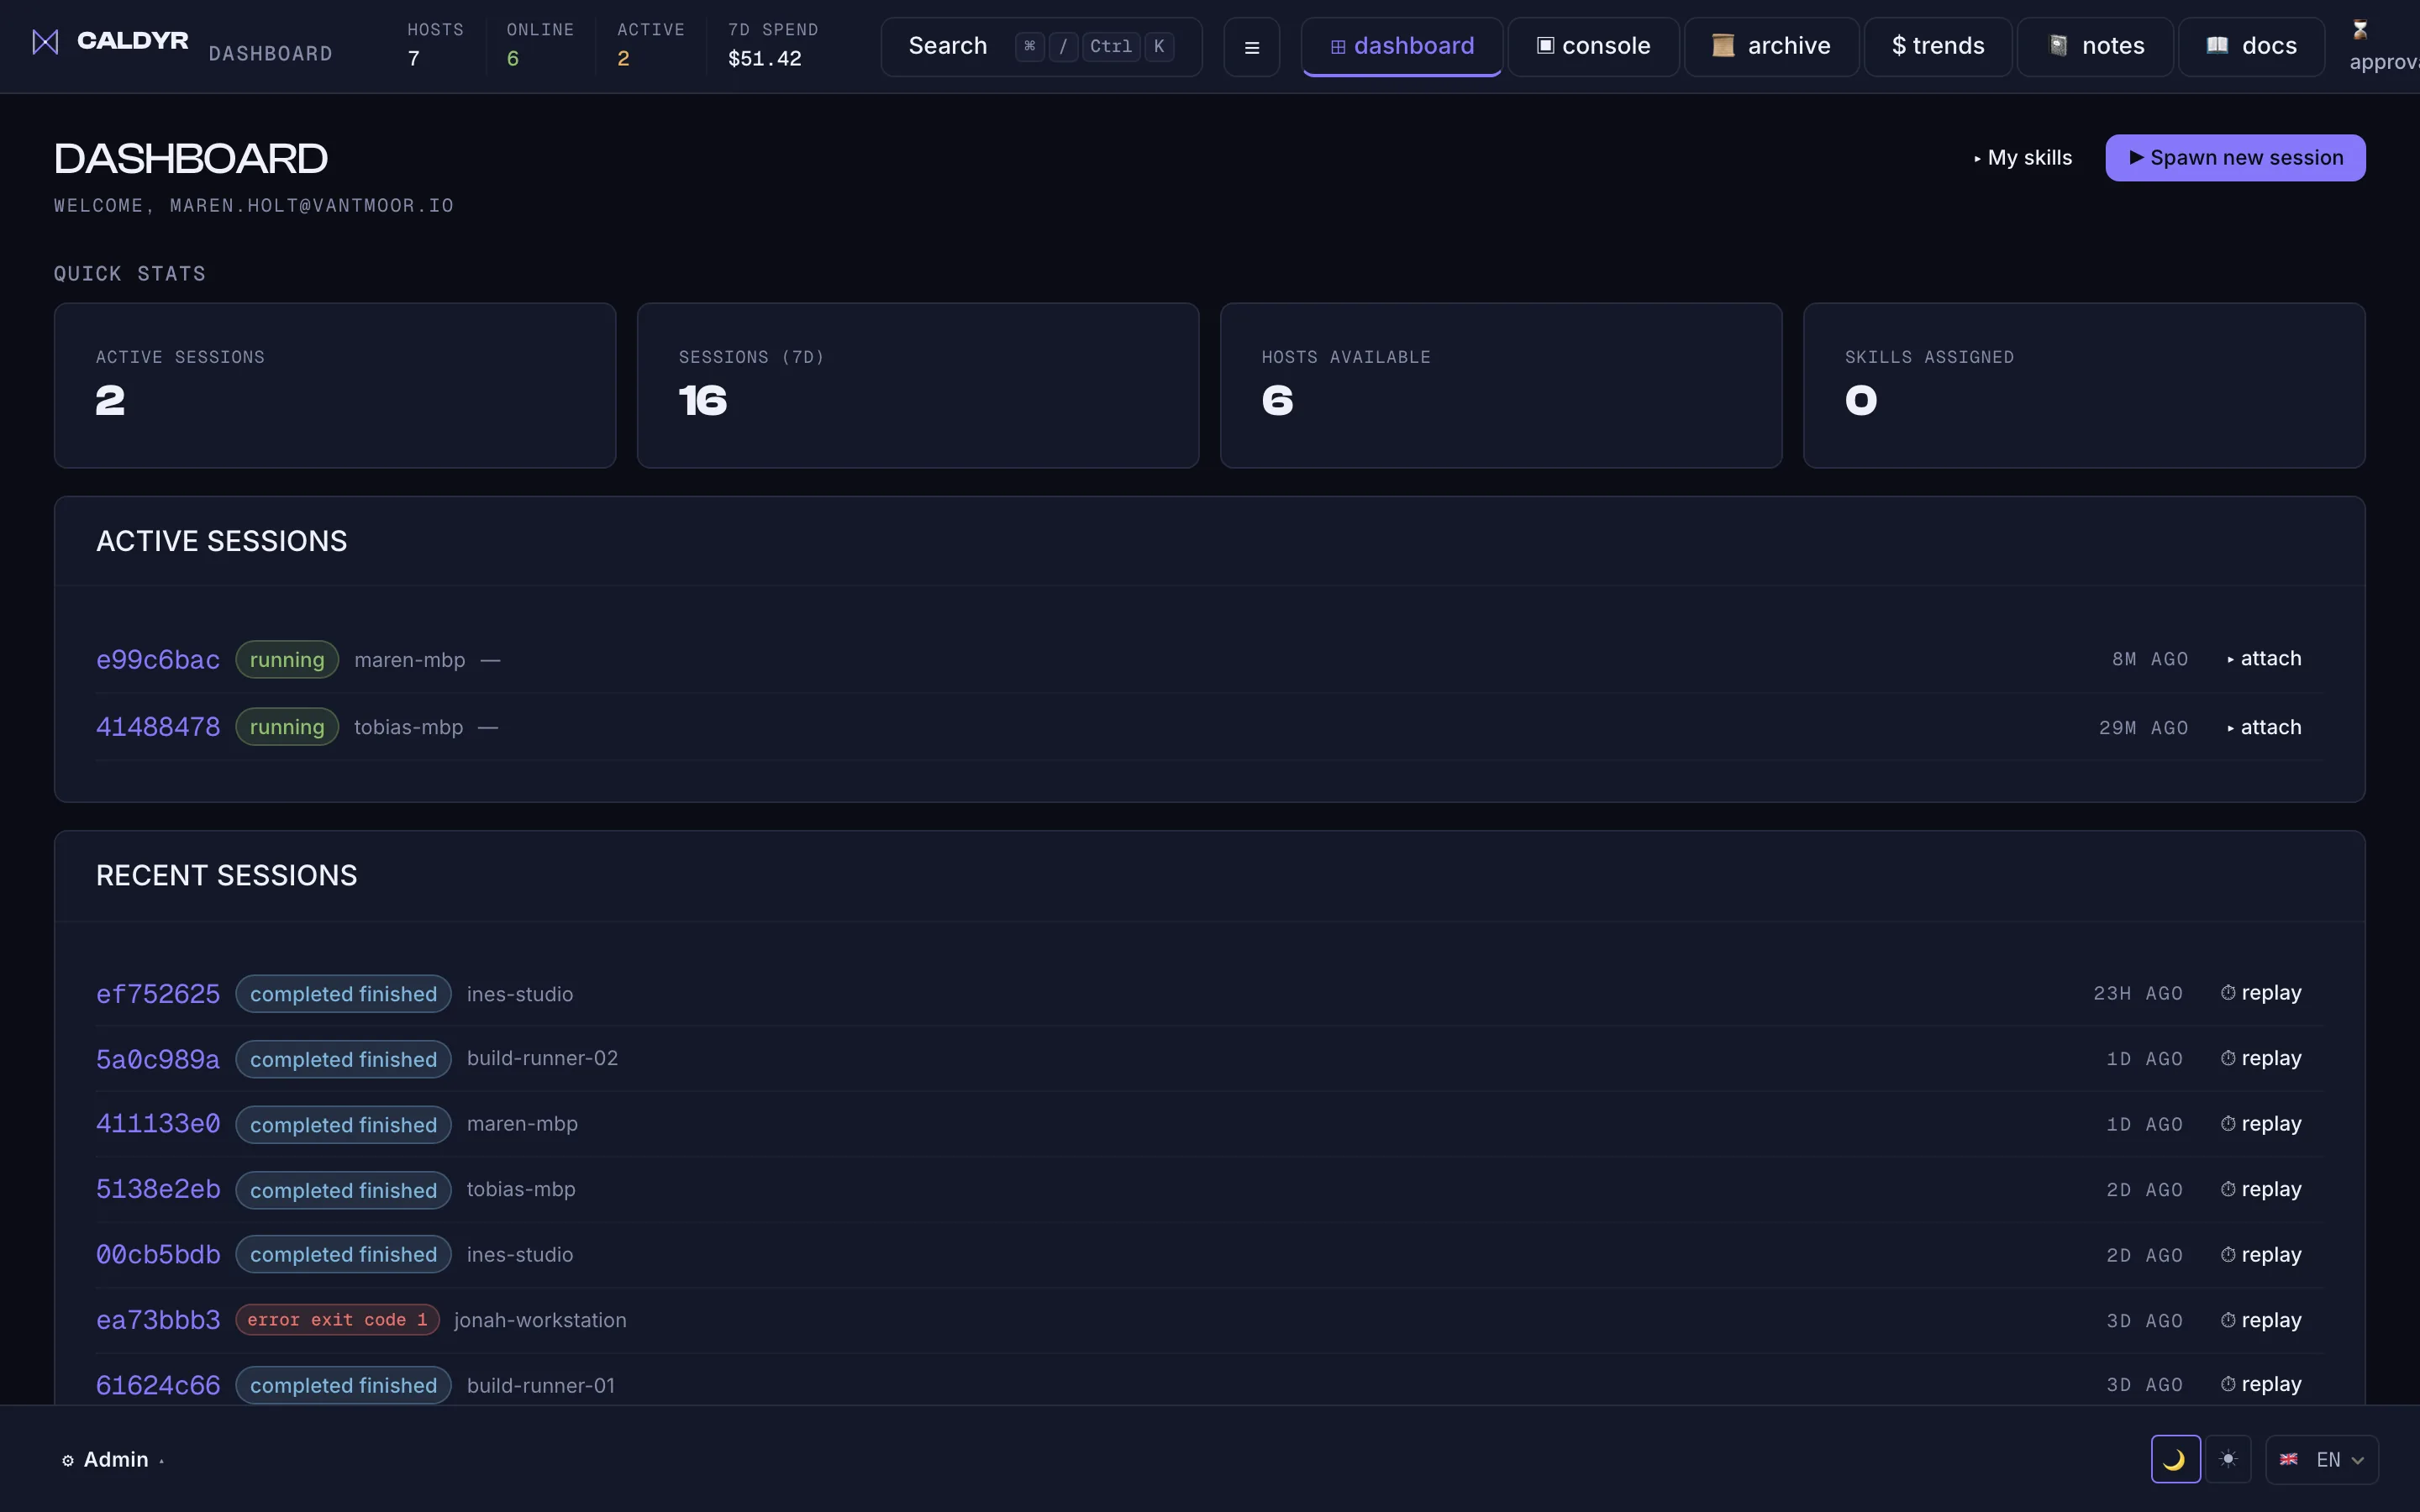
One audited gate for every AI coding agent you run.
Caldyr connects AI coding agents to your organisation, controls what they may reach and do, records what they did, and gives your operators one auditable control plane.
SeeRecordProve
For leaders · control, custody, proof
Prove control,don't just claim it.
Every AI coding session your teams run is enrolled, isolated, and sealed into a tamper-evident record you can hand to any auditor.
$ curl -fsSL https://caldyr.ai/install.sh | sh -s -- --enrol YOUR-CODE --fingerprint SHA256:rGP1nr5165uRQ5Wg1bg0D3khkt5KA6ODpVhOCHvwJ8M,SHA256:27kS4Cnb3bA7SqtXj+92f1Oq4yT1G2BDwHyi7HqtE1U · the code comes from the Add agent button in the app
Caldyr
Hope is not evidence
AI coding agents at scale expose the risks nobody planned for.
You shipped agents to engineering. Compliance, finance, and your CISO want answers now. Caldyr answers with a signed record you keep, without a new stack.
"My team uses coding agents but I have no audit trail."
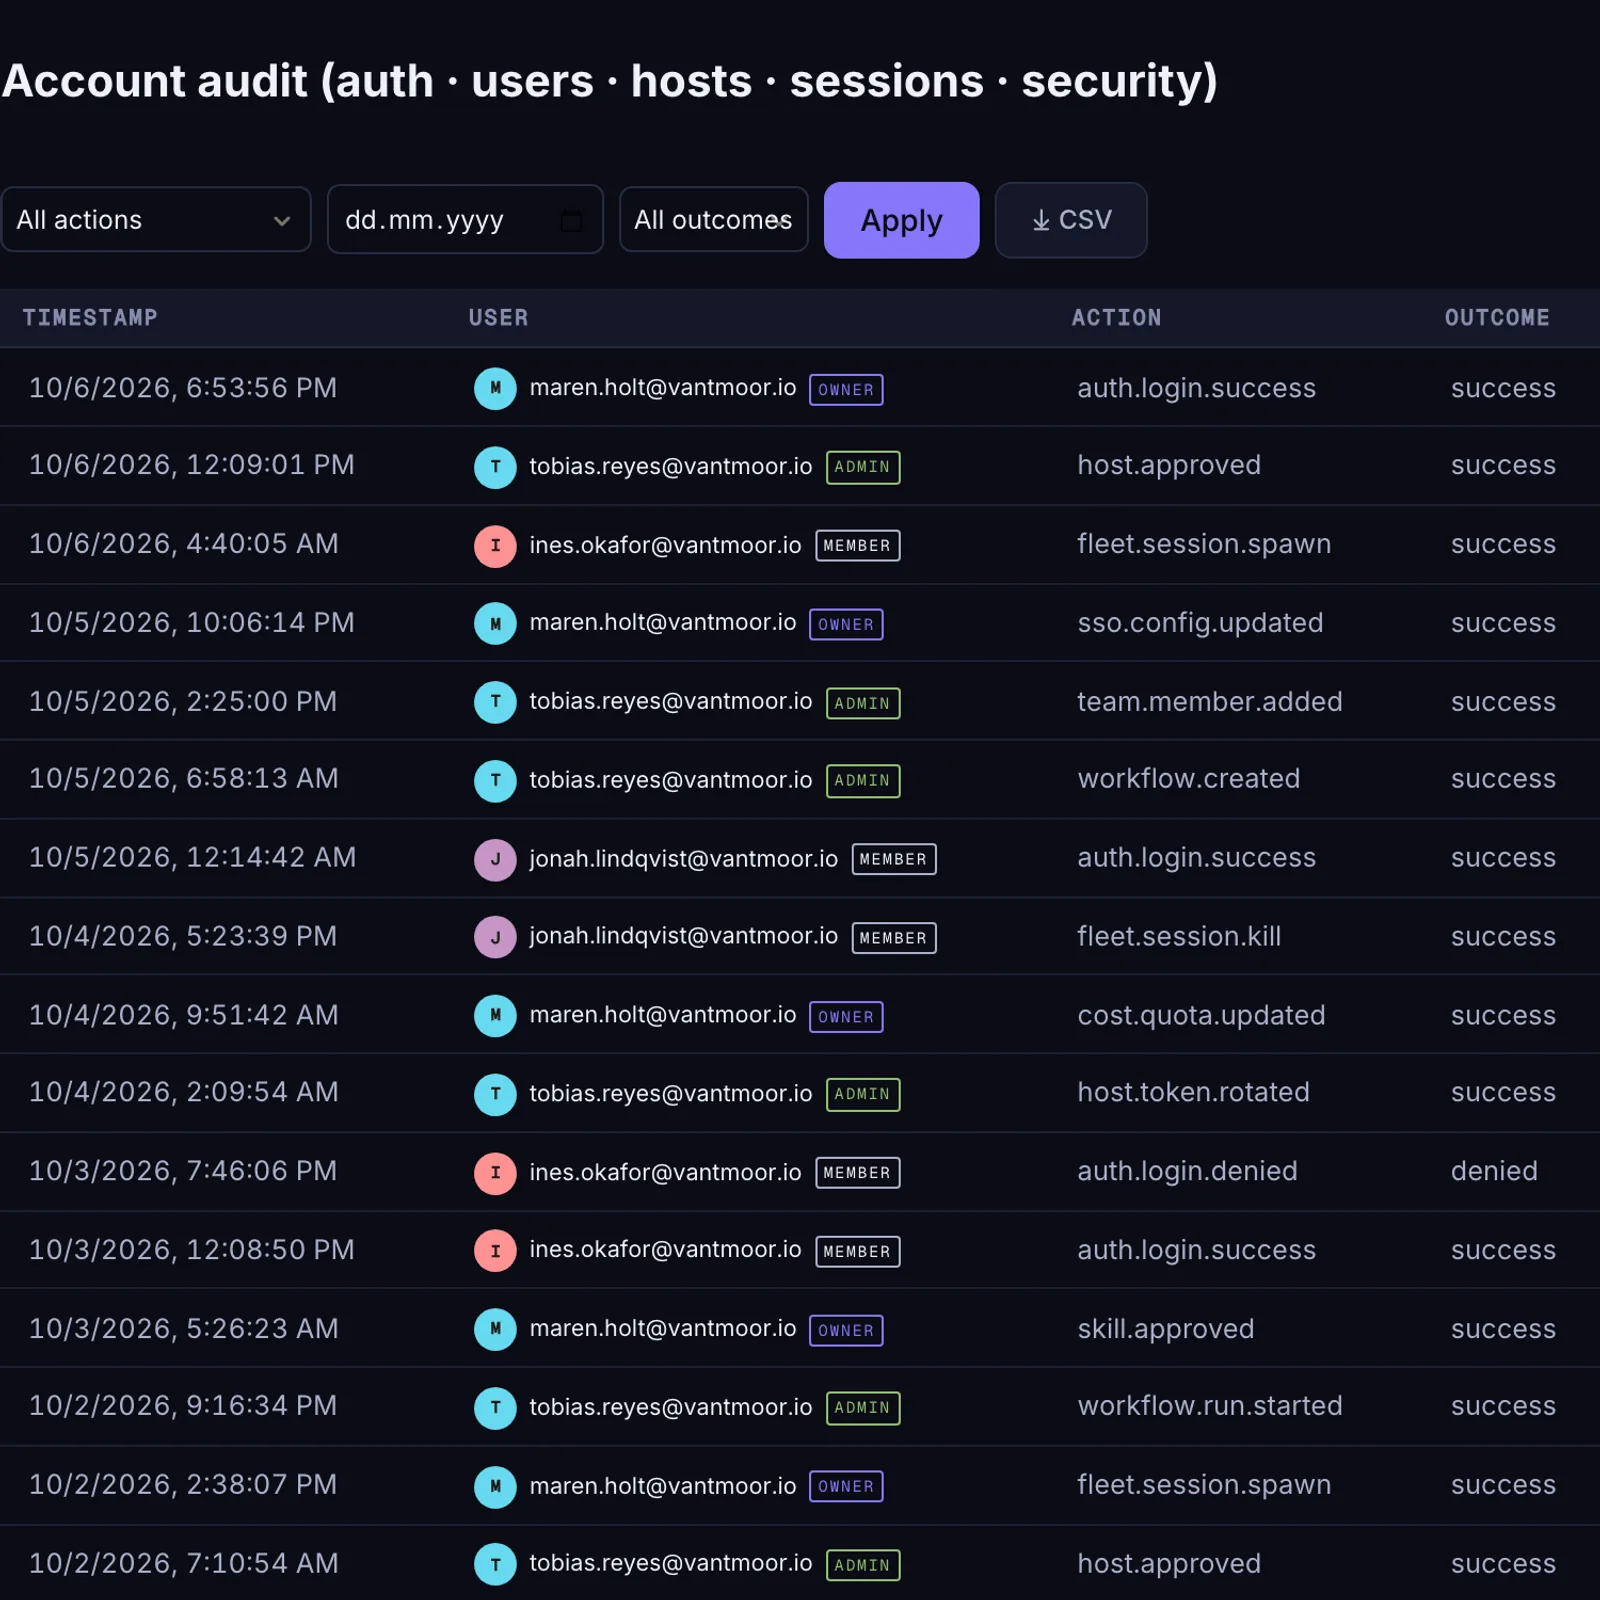
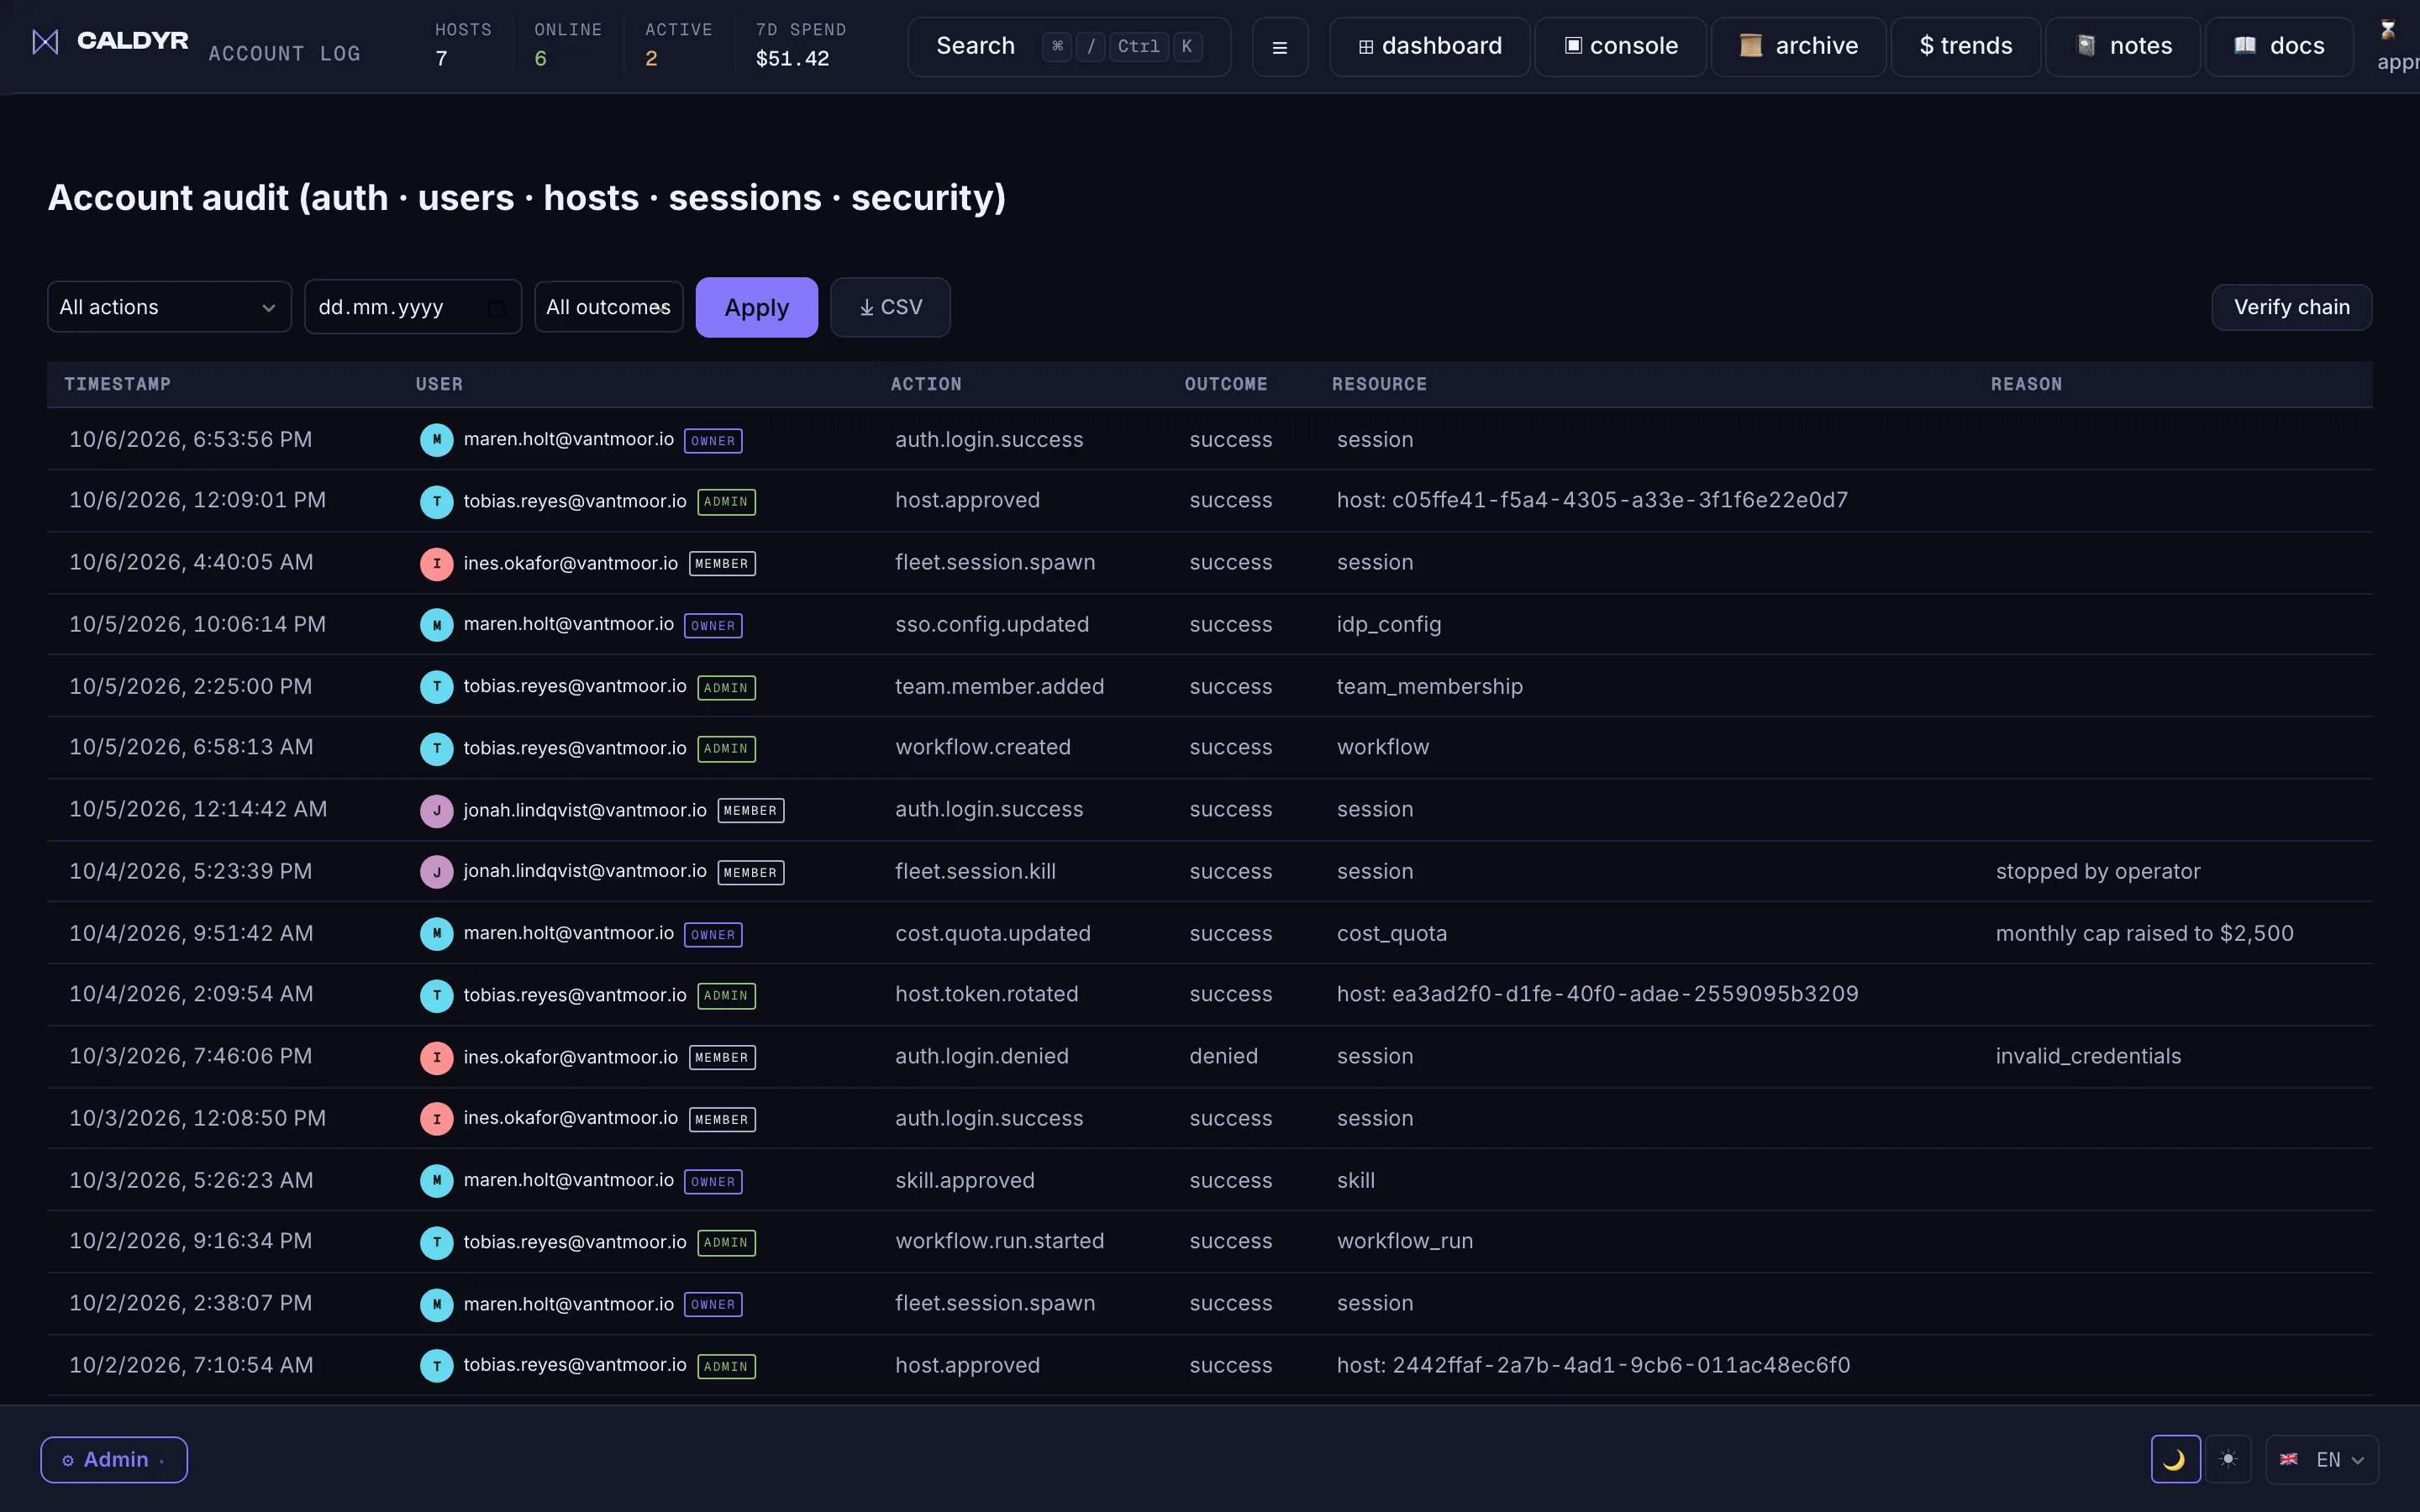
A record you can hand an auditor. Every action your team's AI takes is logged and signed, so you can prove exactly who did what.
Audit signing chain. Every tenant-scoped event is Ed25519-signed and hash-chained — one signature per row, verifiable against your company's own signing key.
"One API key per vendor, shared across the whole org."
Per-team access and budgets. Each team gets its own locked access and a spending cap, so one leaked key or a runaway bill can't hit the whole company.
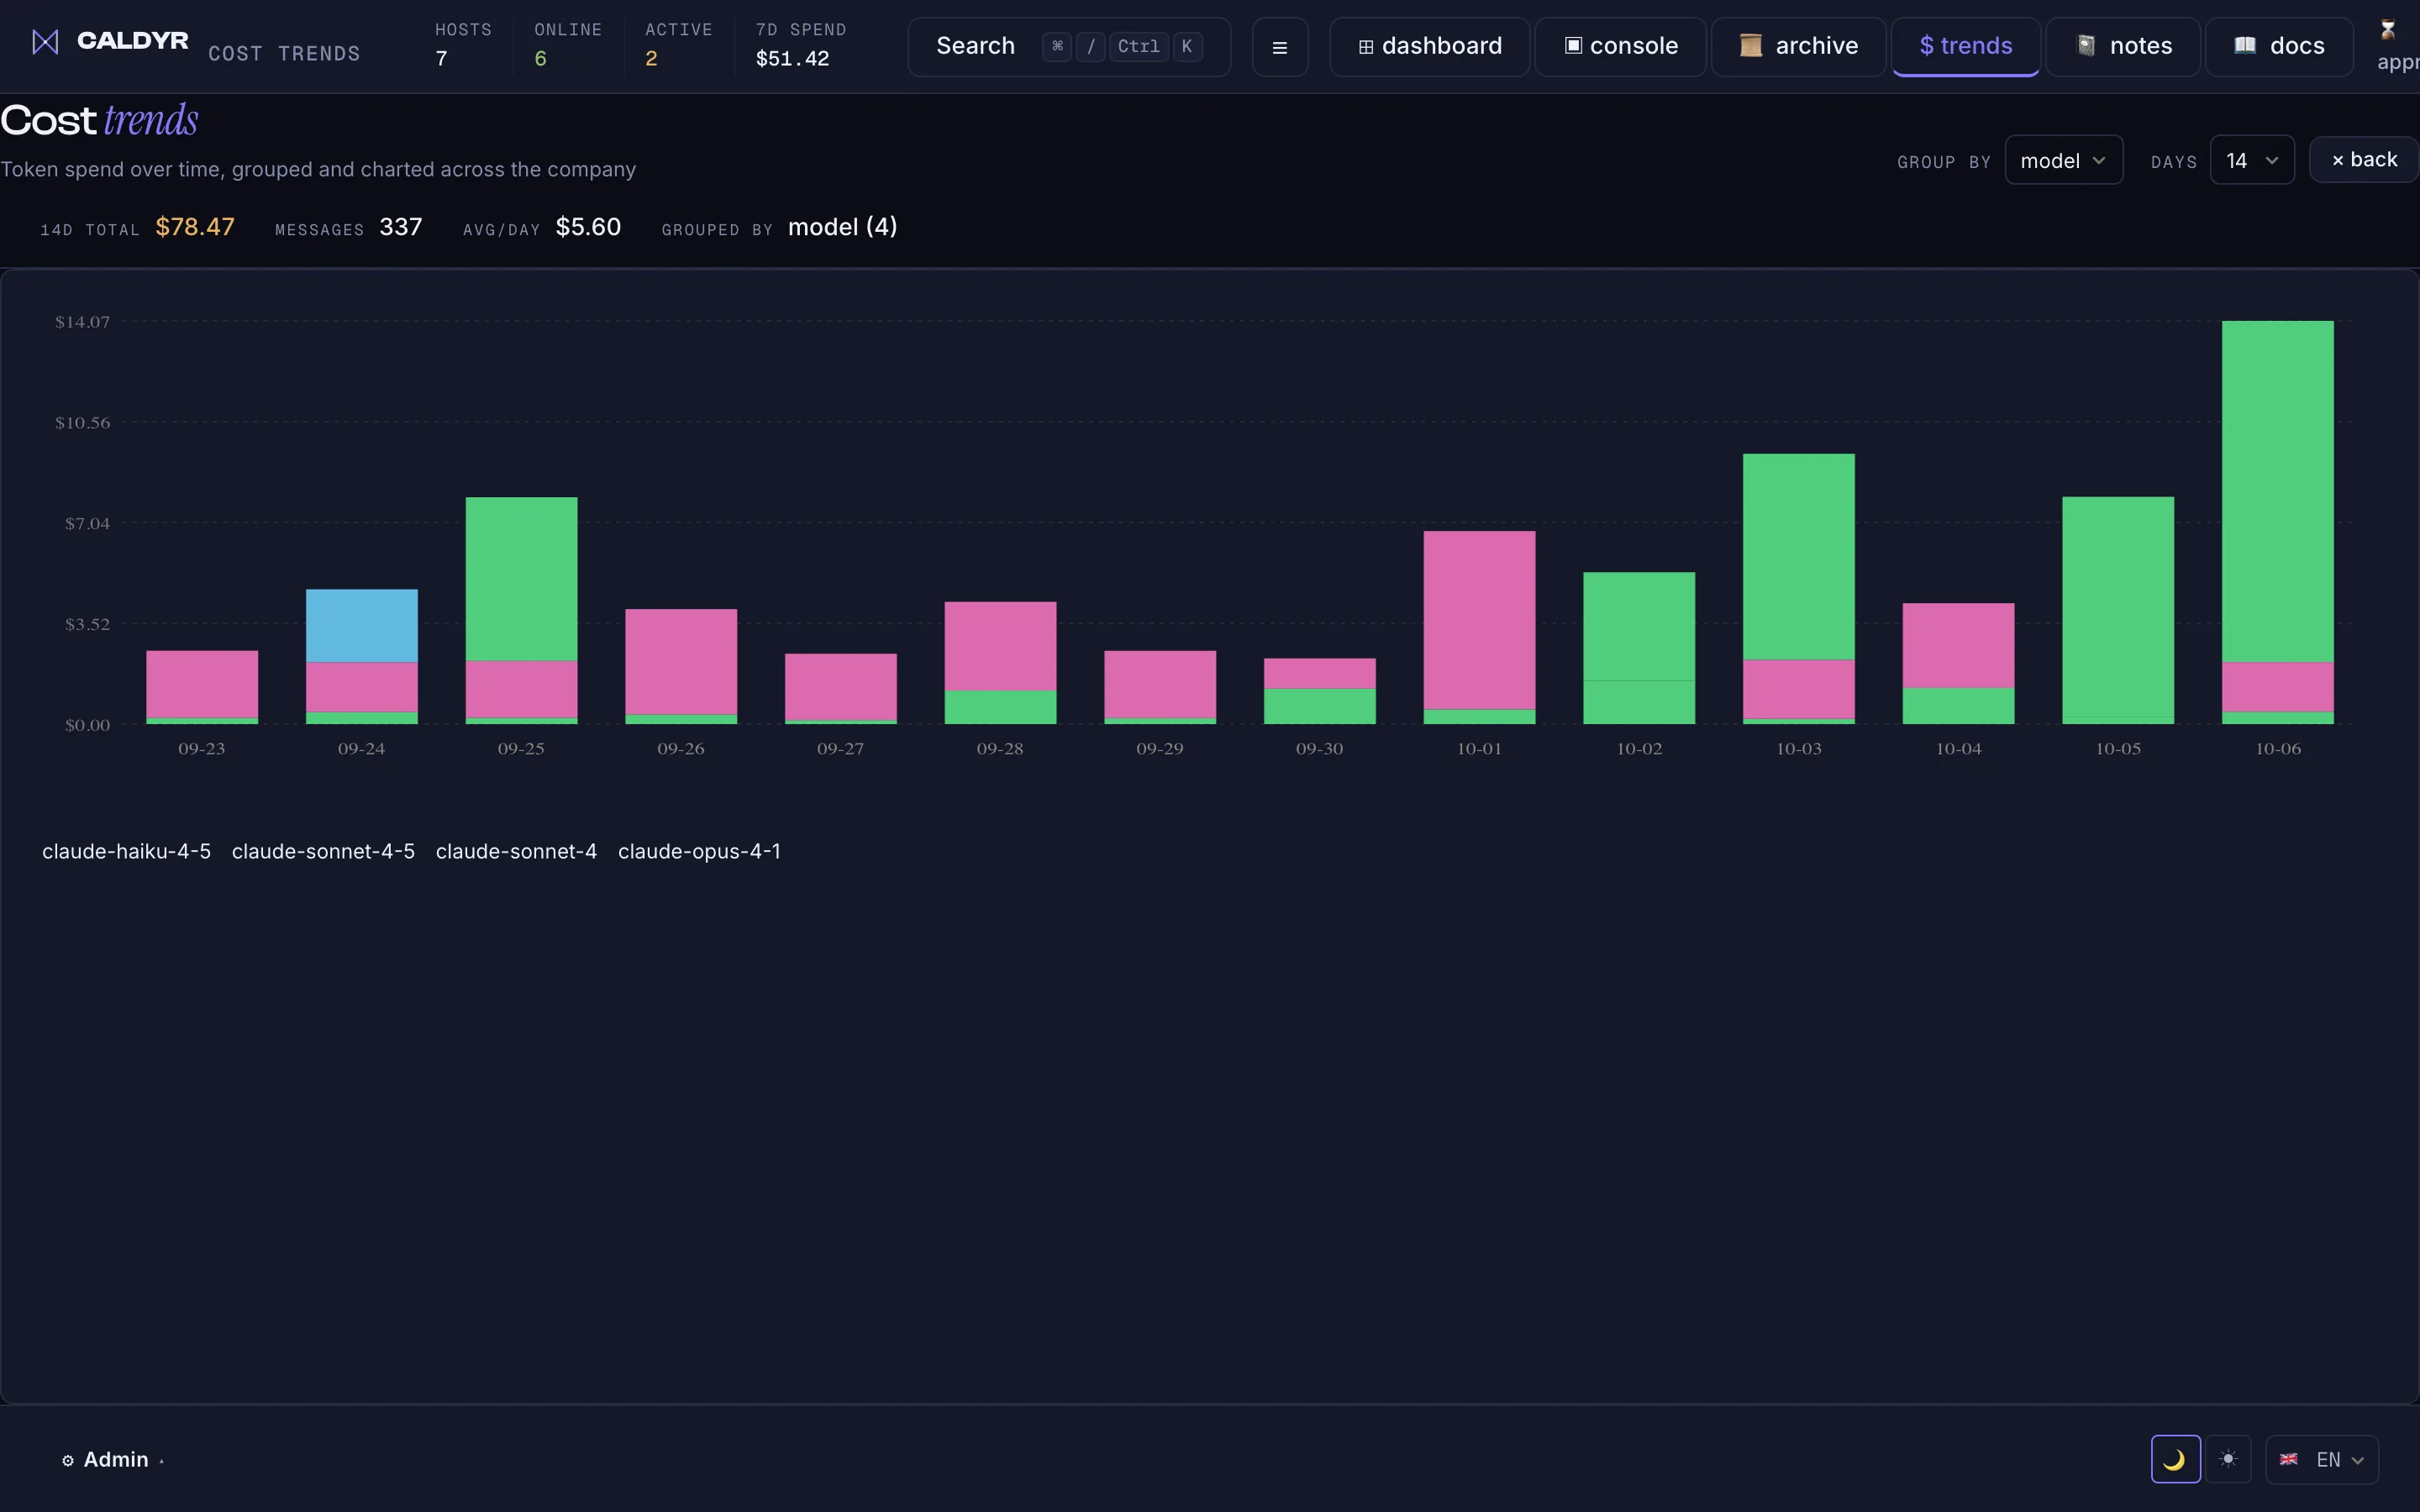
Per-team key, per-team budget. Each team gets its own wrapped key, spend by host, model and label, plus a hard USD cap that blocks new sessions once it is reached.
"Compliance asked for proof we don't leak prompts."
Your data is isolated — and we say what we can see. Your personal vault notes are readable only by you. Your team's secrets, shared knowledge, transcripts and session metadata are isolated per tenant and encrypted at rest under a per-team key our custody service holds, so it can index, search and stream them. The security page lists exactly what we can and cannot see, hosted and self-hosted.
Your personal vault is yours. For the rest, we hold a key. Your personal vault notes are encrypted in your browser under a key derived from your passphrase; we store only ciphertext and cannot recover them if you lose it. Secrets, team knowledge, saved transcripts and session metadata work differently: they reach us readable and are encrypted at rest under a per-team key held by our custody service, which decrypts them to index, search and stream. The security page lists exactly what we can and cannot see.
Regulation is closing in
Built for the rules bearing down on your AI usage.
The EU Cyber Resilience Act, NIS2, SOC 2, and ISO 27001 all demand the same things: proof of who did what, controls you can show an auditor, and data you actually keep. Caldyr hands you the evidence, not another policy PDF.
EU CRA
Signed, tamper-evident records of every AI session: the audit trail the Cyber Resilience Act expects.
NIS2
Access control, isolation, and incident-ready logs for the systems NIS2 puts in scope.
SOC 2
Evidence for your own SOC 2 audit: a signed audit trail of sessions, secret access and policy changes.
ISO 27001
Key management, encryption, and access records that map to Annex A controls.
GDPR
Your personal vault notes are end-to-end encrypted, so we can't read them. Secrets, team knowledge, saved transcripts and session metadata are encrypted at rest under a per-team key held by our custody service, which can decrypt them on request.
Caldyr provides technical controls and audit evidence to support these frameworks. It is not itself a certification; certification remains yours to obtain.
The threshold
Everything you need to keep AI under control, and prove it.
Everything a platform team needs to gate, watch, and seal every AI coding agent.
Complete audit trail
Audit signing chain
A tamper-evident log of your team's actions: every entry carries its own signature, so you can show an auditor exactly who did what.
Ed25519 signs every tenant-scoped audit row — one signature per row, hash-chained per company and per solo user. Verify any range against that chain's own key. Platform-scope rows have no tenant key and are out of scope.
Sends a signed record of activity straight into the security tools your team already uses.
Stream signed audit events to Splunk, Datadog, Elastic, Microsoft Sentinel, syslog, a generic HTTPS webhook, or S3 WORM. Per-destination auth - none, bearer, mTLS, signed JWT or Sentinel OAuth2 - with retry and backoff. Enterprise plan.
People sign in with your existing company login; access is granted and revoked automatically.
OIDC sign-in with any standards-compliant IdP, such as Okta, Azure AD or Google. Optional just-in-time provisioning on first sign-in. SCIM 2.0 for the full user lifecycle (Enterprise).
See spend per team in real time and set hard limits, so AI costs never surprise you.
Spend by host, model and label, with every cost row tied to its team and user. Token cost is attributed per session. Licence seat limits plus configurable USD caps that block new sessions, notify, or warn on breach.
Build repeatable multi-step AI tasks your team can run and watch, kept isolated per team.
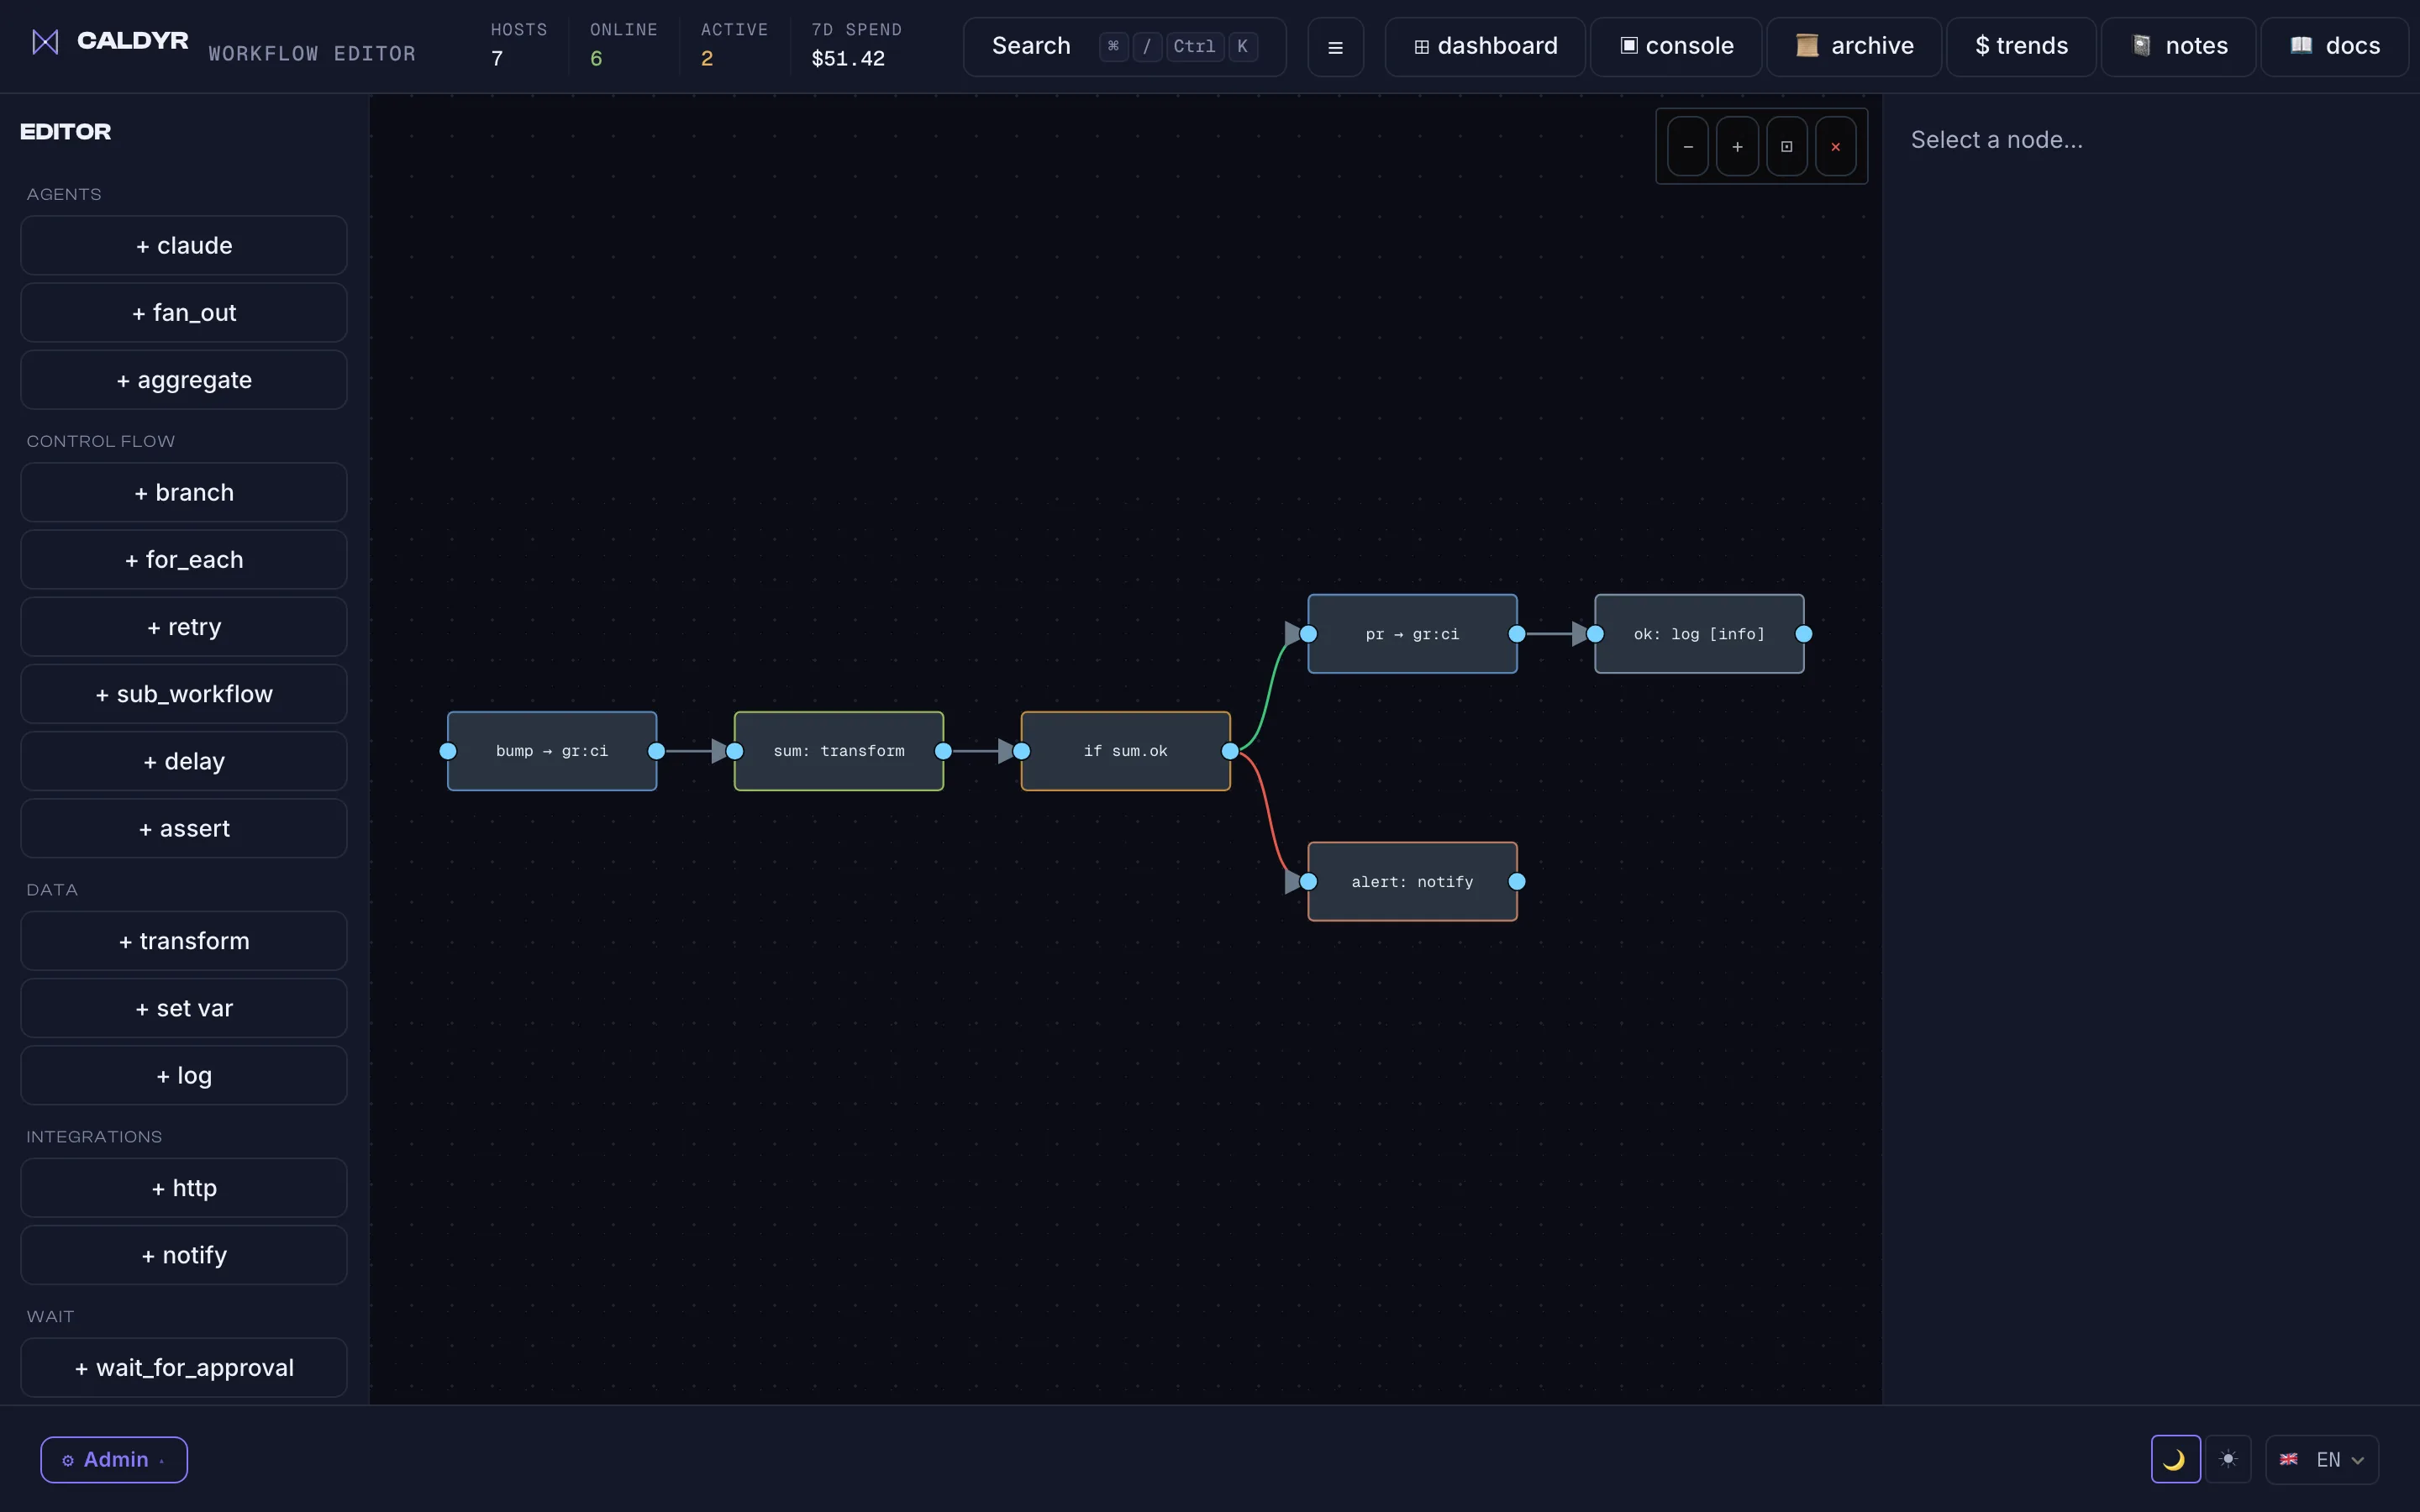
Wire typed nodes — claude, http_request, assert, wait_for_approval, sixteen in all — into a DAG, validate it, run it, and watch the run record live. Starter templates and a visual canvas. Isolated per team; a claude node's timeout sends SIGTERM.
Sealed sessions are off by default. Enable them per company; once enabled, outbound network access from a session is denied.
Opt-in per-company policy to run agent sessions in an isolated network namespace (netns). Egress is denied by default, apart from the agent's own model API and DNS, so an agent can't exfiltrate over the network. Linux hosts only. Default off.
Daemon over HTTPS, one-time code, admin approval, per-host token.
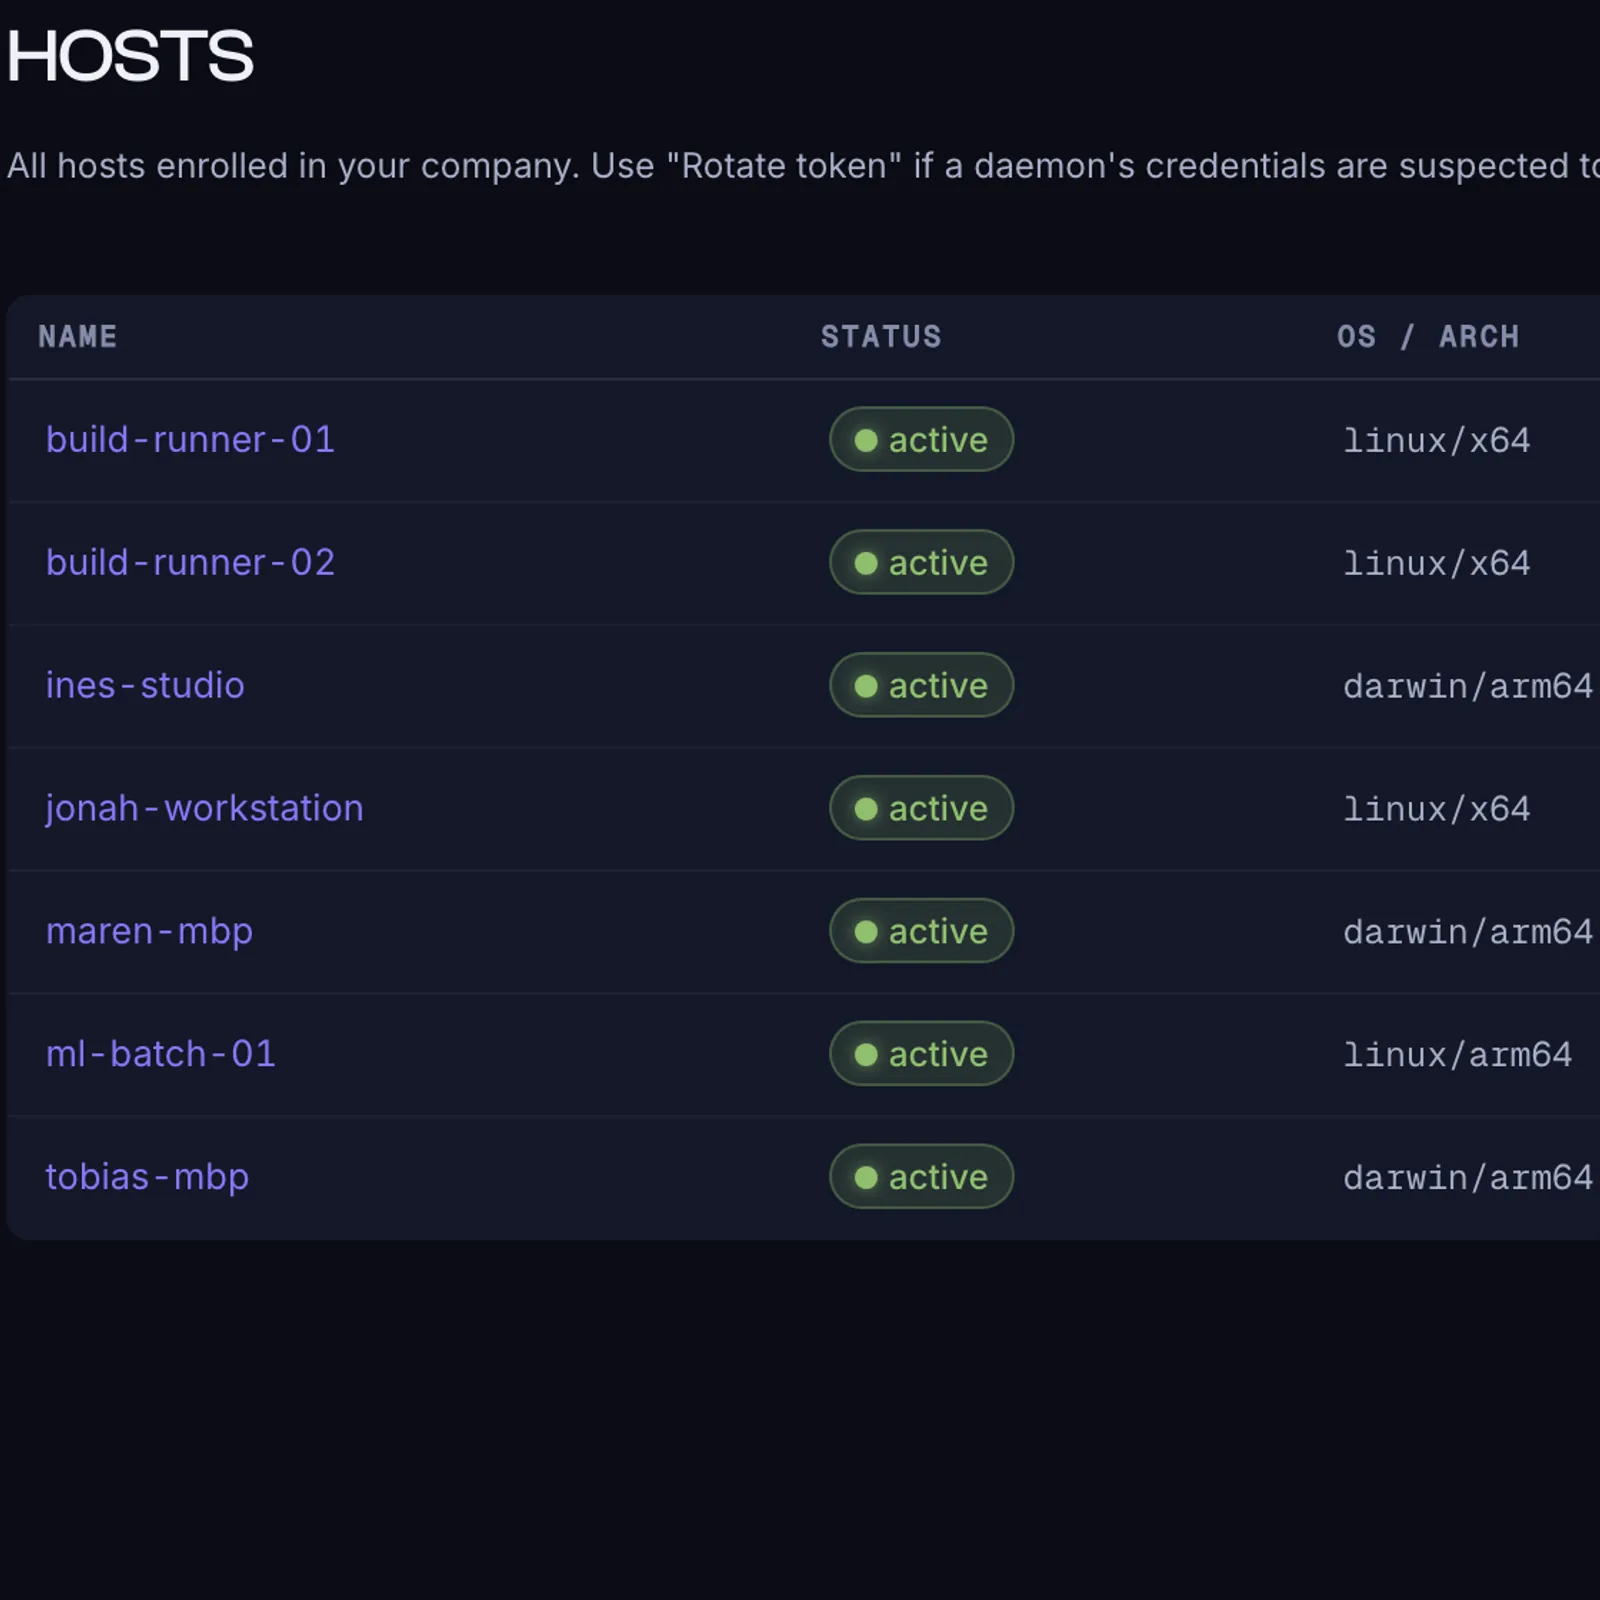
The daemon reaches the hub over HTTPS and checks the hub's certificate. A one-time code from the Add Agent page starts enrolment: the daemon generates a host keypair and sends it with the code, then waits. An admin approving the host is what mints that host's own token.
· Enrolling (waiting for approval on the Add Agent page)…
✓ Online · your-host joined the fleet
2
Spawn per team
Any backend, per-team isolation, admins manage: don't snoop.
Team members spawn agent sessions on any backend, scoped to their team. Row-level security isolates every row, so admins manage access; they don't snoop on your prompts.
SAMPLE
team
session
status
payments-api
cl-9832
live
payments-api
cl-9840
live
◐ other teams' rows — RLS-hidden from this admin
3
Watch + replay
Live xterm stream, frame-by-frame replay, permission events.
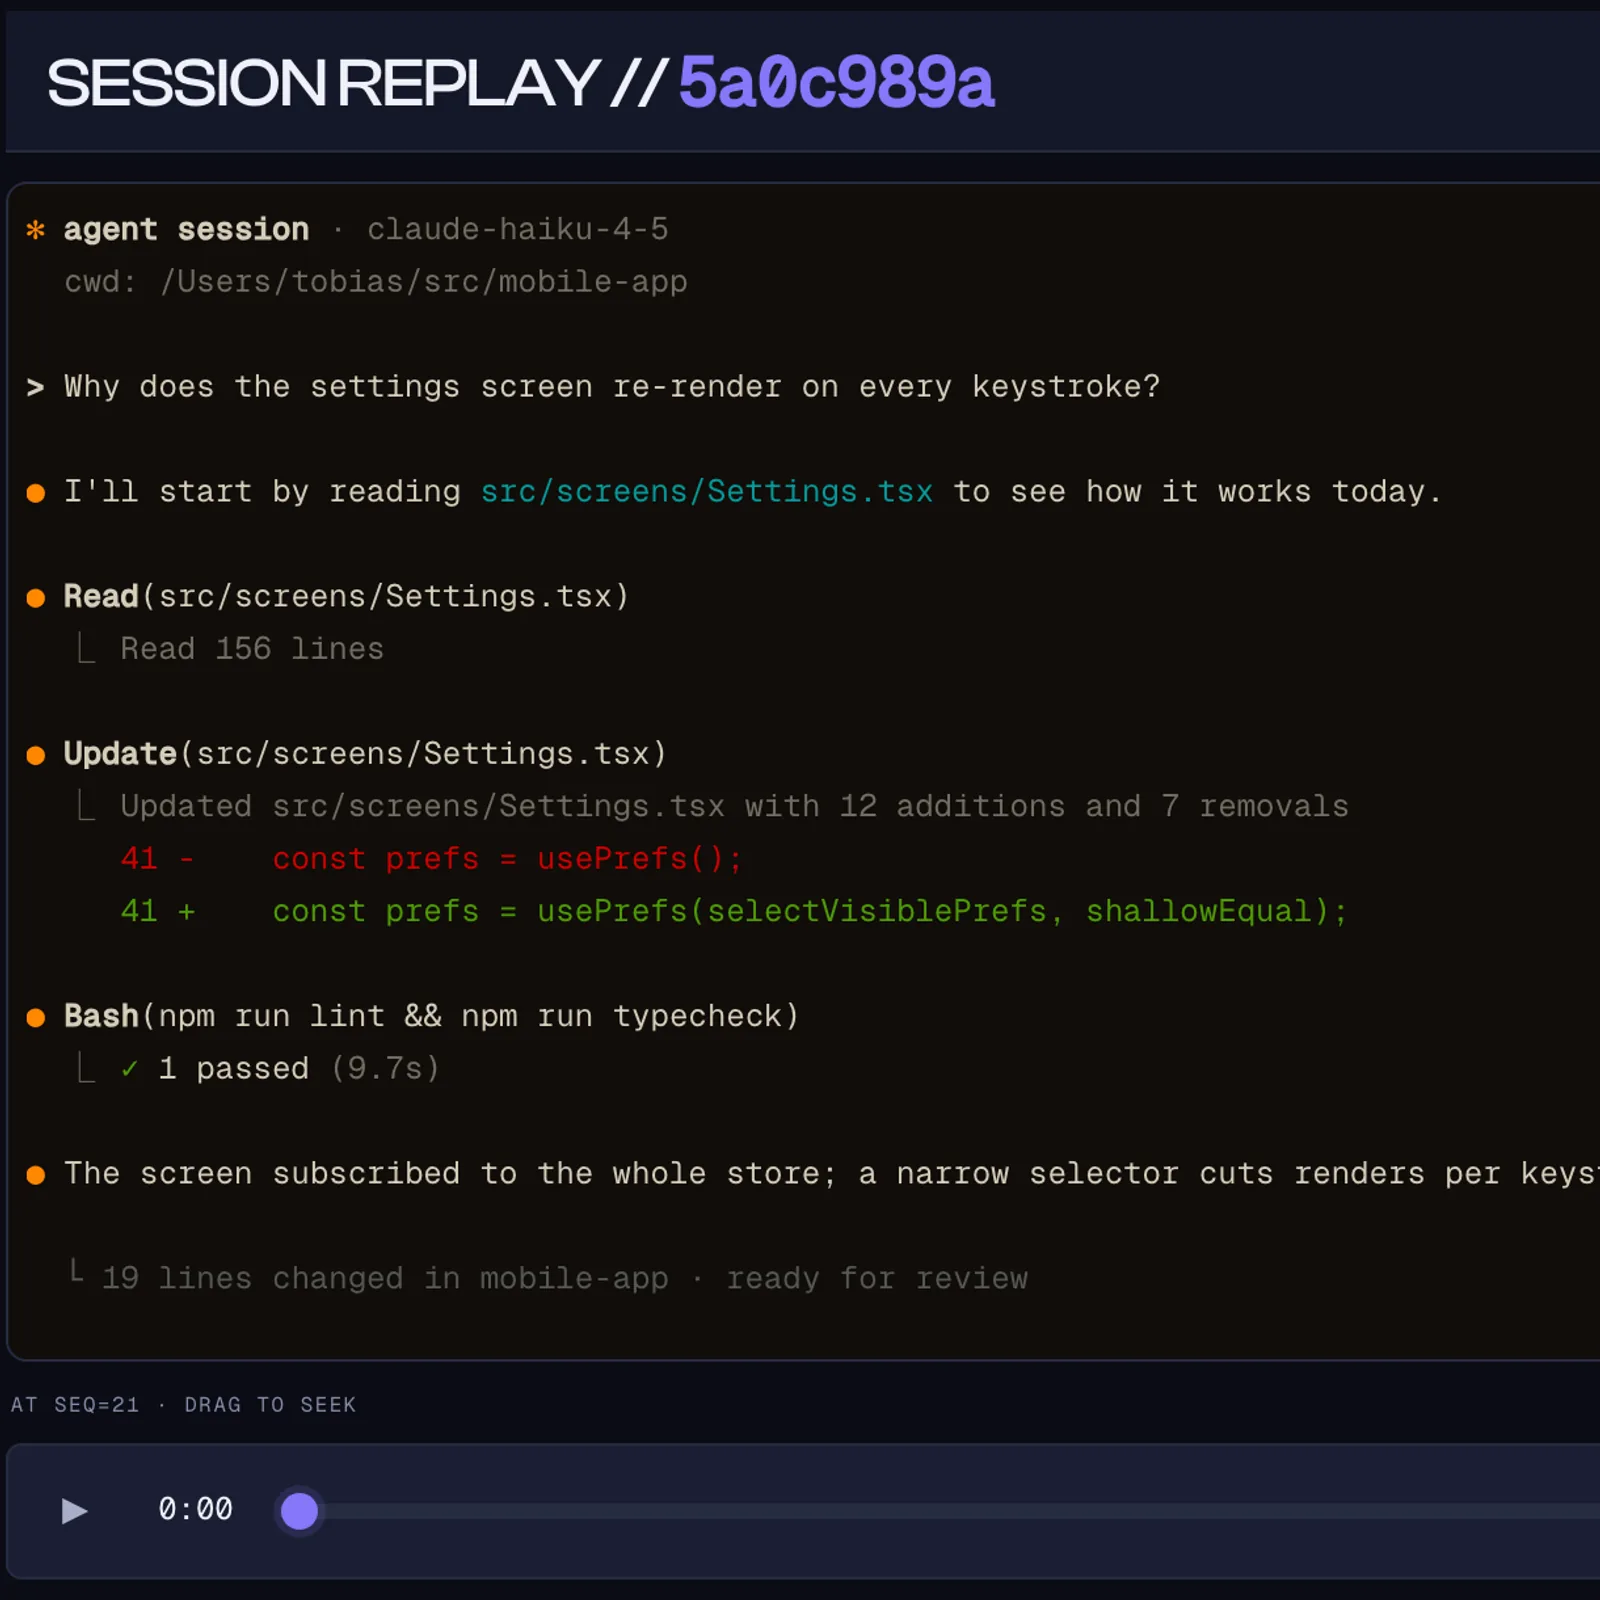
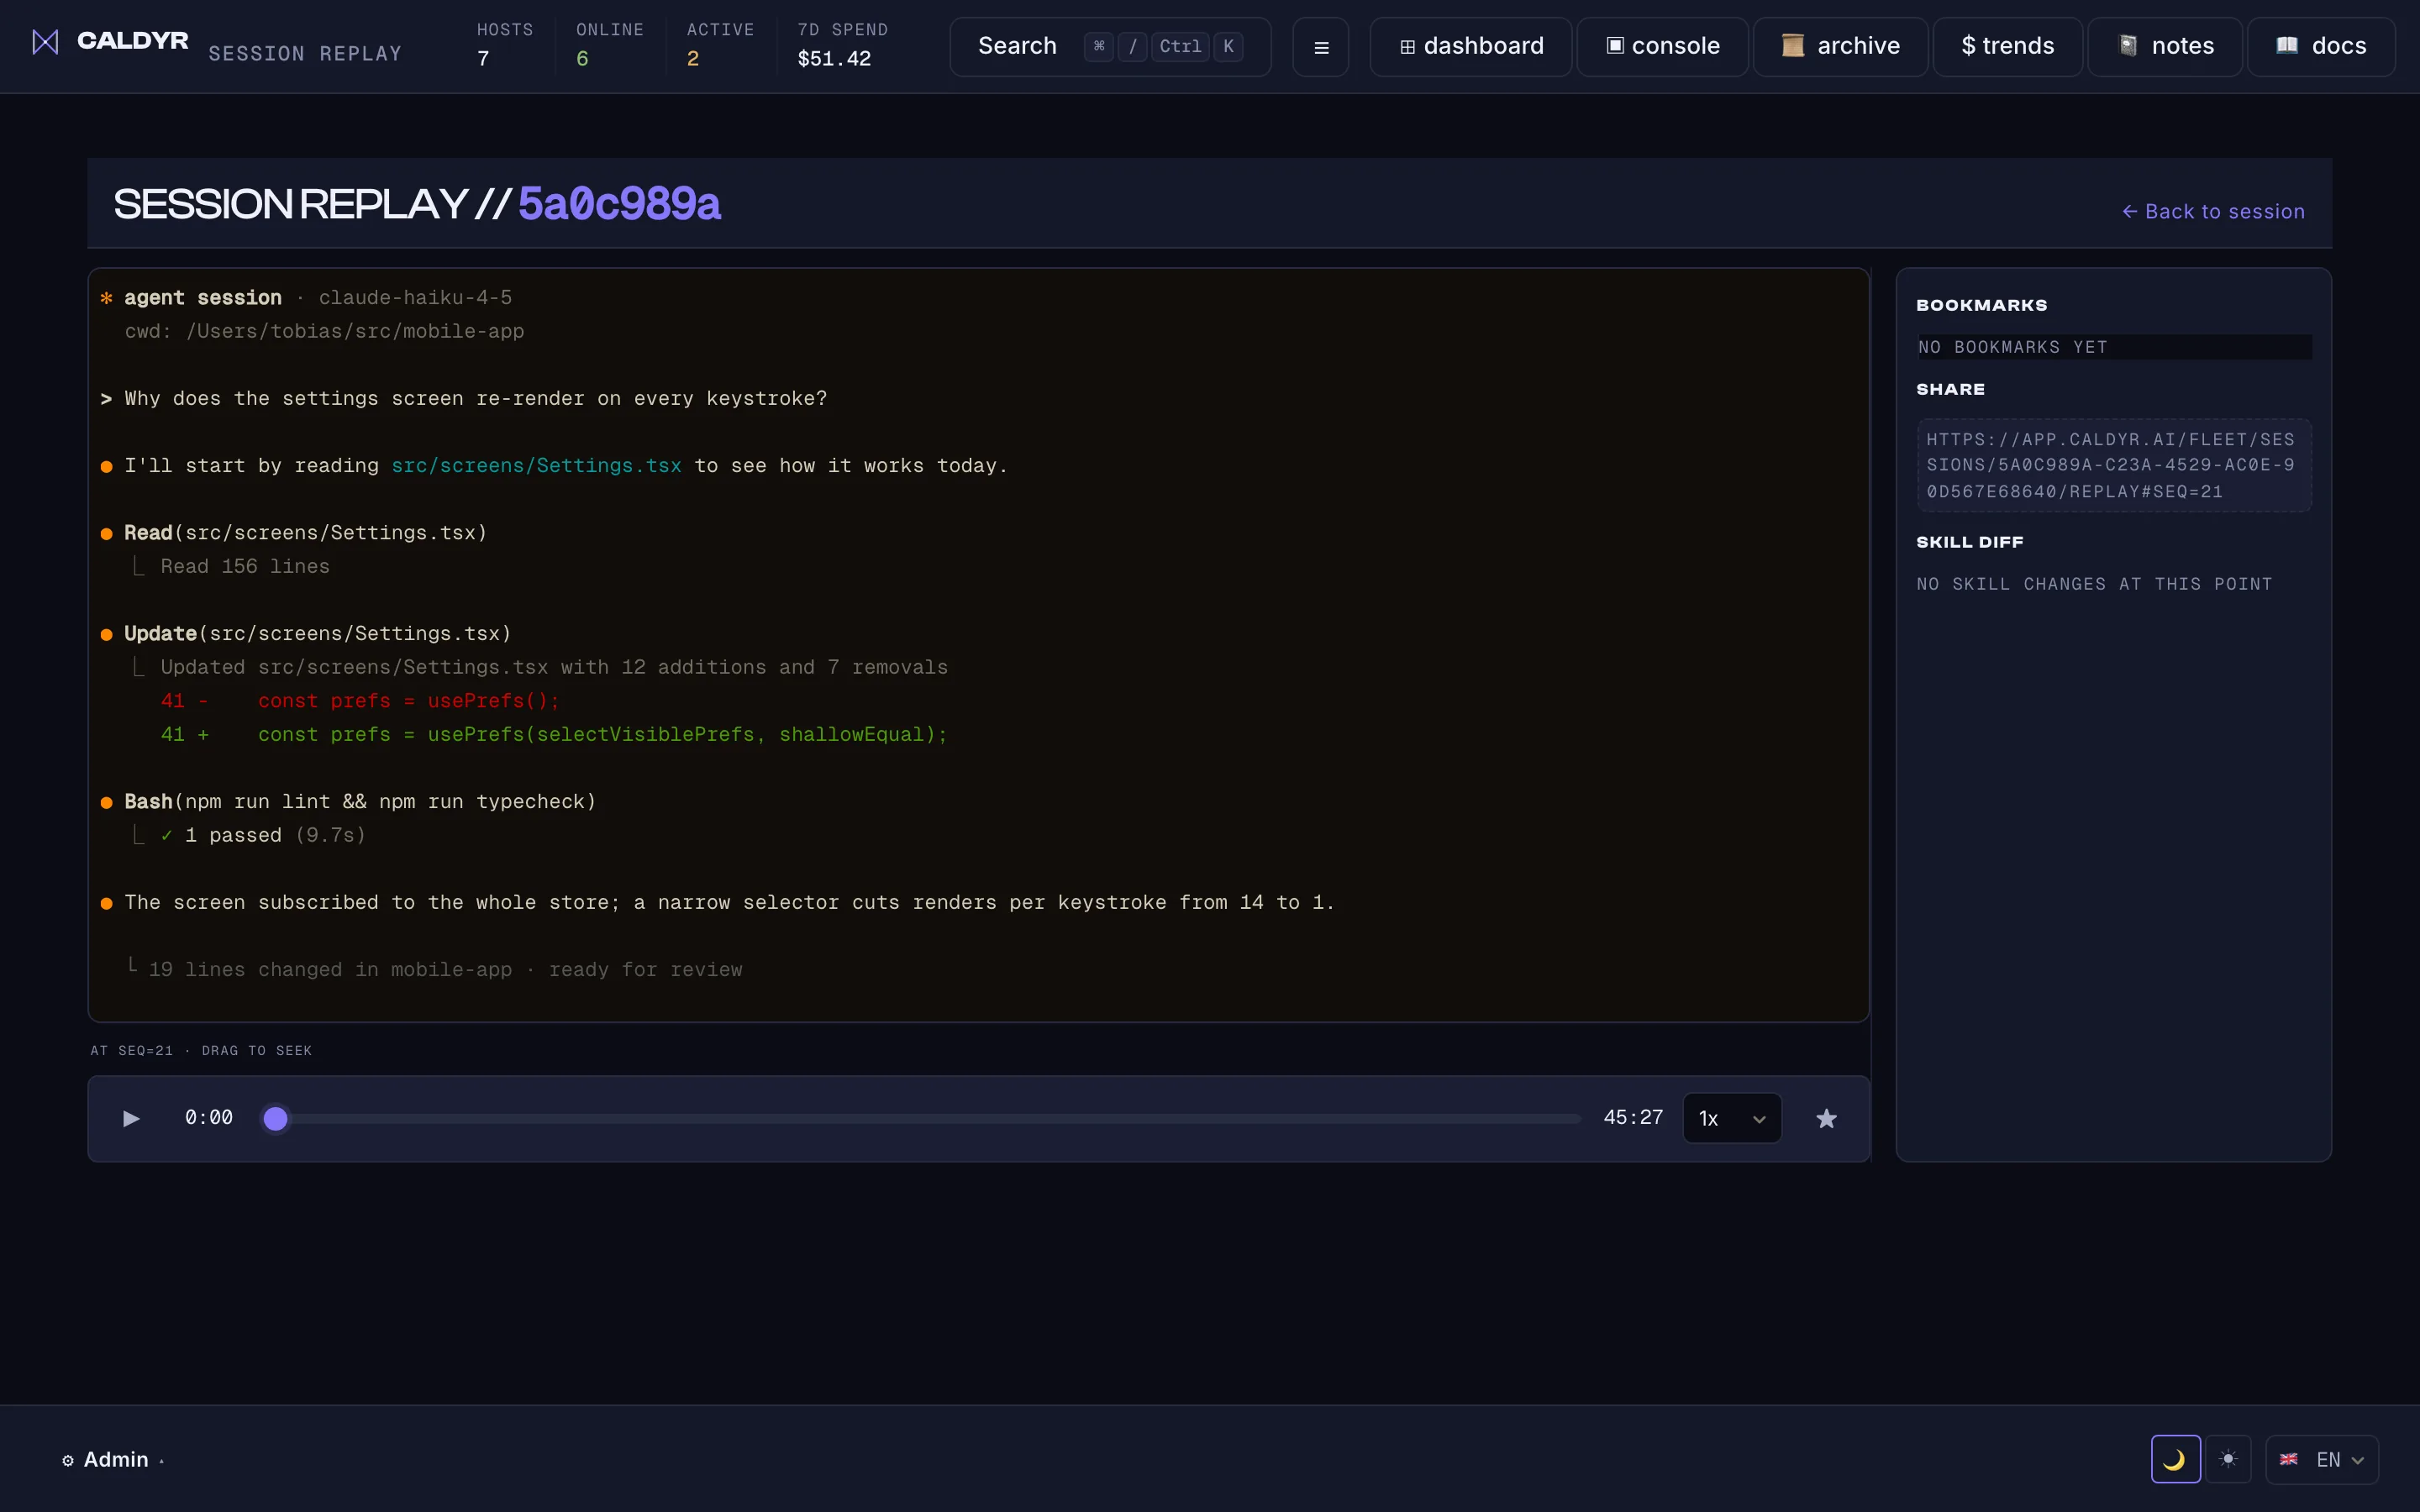
Watch sessions live over an xterm stream, then scrub frame-by-frame in replay with bookmarks. Every permission event lands as a marker on the timeline.
SAMPLE
$ deploy hotfix to prod-backend-eu
⚙ permission requested: bash write
✓ approved by admin · 00:42
⚙ Bash $ kubectl rollout restart
4
Prove + bill
Signed audit to SIEM, per-repo USD attribution, hard caps.
Every action is signed and pushed straight to your SIEM (Enterprise plan). Per-repo USD attribution and hard spend caps land before the invoice does.
Zero third-party telemetry: the control plane phones nothing home
SAMPLE
Verify it yourself
A real 5-row sample audit chain, embedded right in this page. Recompute every SHA-256 hash, check every Ed25519 signature, live, in your browser, right now.
ts
event
prev_hash
hash
sig
status
2026-06-30T09:12:04Z
session.spawn
00000000…000000
1fc9478e…d23310
OyglWI4l…HbCQ==
·
2026-06-30T09:14:51Z
permission.approved
1fc9478e…d23310
f51cd7d3…62b875
DJELgYNW…mFBQ==
·
2026-06-30T09:21:37Z
secret.access
f51cd7d3…62b875
0951657e…440f92
kkygR5aa…eyBA==
·
2026-06-30T09:44:02Z
policy.updated
0951657e…440f92
5fd659a7…20aa98
e4dkZY5U…lkCA==
·
2026-06-30T10:03:19Z
session.closed
5fd659a7…20aa98
99022532…b4952f
MFUtvbrJ…6vCw==
·
Not verified yet; press Verify chain.
Honest comparison
If you've evaluated alternatives, here's how we line up.
Anthropic Console
Caldyr
Per-team budgets
◐ org only
✓
Audit signing chain (Ed25519)
✗
✓
SIEM push (Enterprise)
✗
✓
Self-host air-gapped
✗
✓
End-to-end encrypted personal vault
N/A
✓
Session replay (xterm)
✗
✓
SCIM 2.0 provisioning (Enterprise)
◐
✓
Time to first agent
hours
≈ 10 min after approval
LLM Gateways
Caldyr
Layer governed
model API request / response
agent execution on the host
Per-session capture + xterm replay
–
✓
Transcript encrypted at rest (per-team key)
–
✓
Signed audit chain (Ed25519)
access logs
✓
Host enrolment + per-team RBAC
–
✓
Cost attribution
per API key
per repo · team · session
Self-host air-gap
some
✓
Complementary, not competitive: gateways route the API traffic; Caldyr proves who ran which agent, on what, under whose key, and caps the spend. Run on top of any gateway.
Build it yourself
Caldyr
Per-team budgets
✗
✓
Audit signing chain (Ed25519)
build it
✓
SIEM push (Enterprise)
✗
✓
Self-host air-gapped
depends
✓
End-to-end encrypted personal vault
depends
✓
Session replay (xterm)
✗
✓
SCIM 2.0 provisioning (Enterprise)
✗
✓
Time to first agent
weeks
≈ 10 min after approval
Who answers at the gate
Built for the people who answer for your AI tooling.
Platform teams
You support engineers, not write all the code yourself. You need governance without becoming the bottleneck.
You answer to auditors for CRA, NIS2, SOC 2 and ISO 27001. You need cryptographic evidence: a signed record, not policy PDFs. SIEM streams that prove a negative.